Jekyll-based static website template for security page scenarios
HTMLStarter
security-template — HTML Starter Template
By EdOverflow
SecurityTemplate is a Jekyll-based static website template for building security pages, including pages for security policies, advisories, vulnerability reporting, and a hall of fame.
Explore the design
Compare the page layouts and mobile experience. Open any screenshot for a closer look.
Author preview
Author-provided preview
Preview provided in the project README.
One original preview is available. Open the full image to inspect the design.
Screenshots show visual appearance; interactive behavior may differ.
Recorded 2026-10-02View source
What stands out
A quick read of the recorded project description.
Built-in page structures for security policy, security advisories, vulnerability reporting, and a hall of fame
Configure company name, security email, and HackerOne and Bugcrowd links via _config.yml
Includes a .well-known/security.txt template file
Comes with sample security advisory posts and an advisory list layout
Licensed under MIT, free to use, modify, use commercially, and distribute
Template Details
SecurityTemplate is a static website template maintained by EdOverflow, aimed at organizations that need to publish security-related content. The template is powered by Jekyll, and the repository already includes a complete directory structure: index.md for writing the security policy, advisories.md for listing security advisories, report.md for providing vulnerability reporting contact information, hof.md as the security hall of fame page, plus 404.html, an assets directory, _layouts and _includes layout files, sample advisory posts under _posts, and a .well-known/security.txt template.
To use it, clone the repository, modify the variables in _config.yml and the content of each page, then publish to GitHub Pages or your own server. _config.yml can configure the company name, security contact email, HackerOne and Bugcrowd links, and the Bugcrowd embedded form ID; when a HackerOne or Bugcrowd link is provided, the /report page will automatically redirect, and the Bugcrowd embedded submission form can also be enabled.
The template author describes it as a work-in-progress project that is evolving rapidly, and the README does not provide information on production validation, performance, or compatibility. The repository uses the MIT license, but third-party assets such as demo images, fonts, and icons need to be checked separately for their licenses.
HTMLLauncher
Is it right for your project?
Use Cases
- Build a public security policy page for an organization
- Centrally publish and display security advisories
- Provide a vulnerability reporting entry point and redirect to HackerOne or Bugcrowd
- Create a hall of fame page for security researchers
- Declare the vulnerability disclosure process via security.txt
Suitable For
- Teams that need to quickly set up security policy and advisory pages
- Organizations using GitHub Pages to publish static sites
- Projects that want to use HackerOne or Bugcrowd as the vulnerability intake channel
- Users who accept modifying content on top of a Jekyll template
Getting started & customization
Use these recorded setup notes alongside the repository instructions for your chosen version.
- 1
After cloning the repository, modify variables such as company_name and email in _config.yml
- 2
Replace the content in index.md, advisories.md, report.md, and hof.md with actual content
- 3
If redirection is needed, fill in hackerone_url or bugcrowd_url in _config.yml; when using the embedded form, fill in bugcrowd_id
- 4
You can set up a local Jekyll environment for testing by following the GitHub documentation, then publish to GitHub Pages or your own server
- 5
The repository is a work-in-progress project; before use, it is recommended to check the current code and dependency status yourself
License & source material
Usage conditions & limitations
Free to use · keep license noticeThis entry covers the free version in the public repository under the MIT license; the free scope is the code of that version and does not mean that external services or third-party assets are free.
Must comply with when using
- The code of this version may be used, modified, used commercially, and distributed free of charge.
- When distributing copies or substantial portions of the code, retain the original author's copyright notice and the full MIT license notice.
- The code is provided as is; warranties and limitations of liability are governed by the original license and applicable law.
Additional costs & items to verify
- Using the Bugcrowd embedded submission form requires filling in the Bugcrowd ID in _config.yml; this is an optional external service integration, not mandatory.
- If a HackerOne or Bugcrowd link is specified in _config.yml, the /report page will automatically redirect to the corresponding external platform; this is an optional configuration.
- Enabling the Bugcrowd embedded form requires uncommenting and configuring the embed token, and depends on the external Bugcrowd service.
- Demo images, fonts, icons, and other third-party assets need to be checked against their respective licenses and cannot be judged solely by the code's MIT license.
- External services such as domains, hosting, databases, payments, or AI may incur additional charges.
View Original Text Basis
Permission is hereby granted, free of charge
Original License Text
bugcrowd_id` — replace this with your [Bugcrowd ID](https://docs.bugcrowd.com/v1.0/docs/embedded-submission-form), if applicable
Original README
`hackerone_url` and `bugcrowd_url` — the <b>/report</b> URL will redirect to one of these, if specified.
Original README
https://github.com/EdOverflow/security-template/blob/master/LICENSEhttps://github.com/EdOverflow/security-template/blob/master/README.mdYou can also use an embedded Bugcrowd submission form. Just uncomment the form, and add your Bugcrowd embed token under `bugcrowd_id` in `_config.yml`.
Original README
Compiled by DeepSeek based on repository license and README ·2026-10-02. Results only cover the materials read; dependencies, images, fonts, and subsequent term changes are subject to their respective original texts.
Project checks & description sources
Template Information
- Source platforms
- GitHub
- Documentation and maintenance reference score
- Partly documented · 69 / 100
- Technologies
- HTML
- Website type
- Starter
How this score is calculated
Our heuristic uses license records (up to 30), a demo link (12), a preview (10), stars (15), recorded maintenance (15), description completeness (8), feature records (5) and classification data (5). It is not a code, security or performance test, or a Google score. A link does not establish tested functionality.
What to verify for this project
- Repository update recorded
- 2025-07-19
- Screenshot last checked
- 2026-10-02
No demo link is recorded. Use the repository instructions to evaluate the project locally; the screenshot alone cannot establish interactive behavior.
The catalog identifies HTML as the primary stack. Check the actual dependency manifest and lockfile for versions and hosting requirements. These notes use recorded metadata, not a code audit or a deployment test.
Use a selection guide →How this description was prepared
AI-assisted description based on catalog records and repository material. Repository authors are not automatically the reviewers of this description.
Automatically checked against source and license rules; no manual editorial review.
Inspect the recorded source material
SHA-256: e961071cdf33bc1f67e8b2878125c109a5425666d613e894c00a0d35320b0306
2026-10-02T16:11:17.420Z
Source file / repository<div align="center"> <img align="center" src="https://user-images.githubusercontent.com/4115778/32569683-b5075996-c4b9-11e7-8a60-7412bcd7356b.png" height="200"></img> </div> <div align="center"> <br/> </div> <a href="https://www.buymeacoffee.com/edoverflow" target="_blank"><img src="https://www.buymeacoffee.com/assets/img/custom_images/orange_img.png" alt="Buy Me A Coffee" style="height: auto !important;width: auto !important;" ></a> # Project _SecurityTemplate_ is a static website template for security pages, powered by Jekyll. It's easy to get started. Clone this repo, edit the configuration files and content to your liking, and publish with [GitHub Pages](https://pages.github.com) or on your own server platform. You can [set up a local environment](https://help.github.com/articles/setting-up-your-github-pages-site-locally-with-jekyll/) to test your _SecurityTemplate_ static site, and [push to GitHub](https://help.github.com/articles/using-jekyll-as-a-static-site-generator-with-github-pages/) if desired. This project is a rapidly evolving work in progress. We value [contributions](https://github.com/EdOverflow/security-template/blob/master/CONTRIBUTING.md) from the public. # Structure The template directory structure is as follows: ``` . ├── 404.html # 404 page. ├── advisories.md # Security advisories list. ├── assets # Page assets. │ ├── css │ │ └── styles.css │ └── images │ └── icon.png ├── _config.yml # Config file with all your variables. ├── _drafts ├── Gemfile ├── Gemfile.lock ├── hof.md # Hall of fame page. ├── _includes │ └── advisory-list.html ├── index.md # Security policy. ├── _layouts │ ├── default.html │ └── post.html ├── LICENSE ├── _posts │ └── 2017-07-22-cve-2017-0914.md # Example security advisory. ├── README.md └── report.md ```  ## `config.yml` * `company_name` — replace this with your organization name * `email` — replace this with your security contact address * `bugcrowd_id` — replace this with your [Bugcrowd ID](https://docs.bugcrowd.com/v1.0/docs/embedded-submission-form), if applicable * `hackerone_url` and `bugcrowd_url` — the <b>/report</b> URL will redirect to one of these, if specified. ## `index.md` The index file is where your security policy lives. To learn more about writing good security policies, please refer to https://support.hackerone.com/hc/en-us/articles/205624665-How-do-we-write-a-good-policy-. ## `advisories.md` This is where you can list your security advisories. The list is updated every time you add a security advisory to the `_posts` folder. ## `report.md` This file should contain contact information for security researchers to use when reporting a security vulnerability. If a HackerOne or Bugcrowd URL is specified in `config.yml`, users will be redirected automatically. You can also use an embedded Bugcrowd submission form. Just uncomment the form, and add your Bugcrowd embed token under `bugcrowd_id` in `_config.yml`. ## `hof.md` This is your security acknowledgements page. List the details of security researchers that reported valid security issues (and wish to be listed publicly). ## `.well-known/security.txt` `security-template` contains a security.txt template file. _security.txt_ defines a standard to help organizations define the process for security researchers to safely disclose vulnerabilities via a simple text file. For more on this, please refer to https://securitytxt.org/. # Contributing We welcome contributions from the public. ### Using the issue tracker 💡 The issue tracker is the preferred channel for bug reports and features requests. ### Issues and labels 🏷 The bug tracker utilizes several labels to help organize and identify issues. ### Guidelines for bug reports 🐛 Use the GitHub issue search — check if the issue has already been reported.
Explore similar templates
Compare previews and descriptions within the same stack and category.
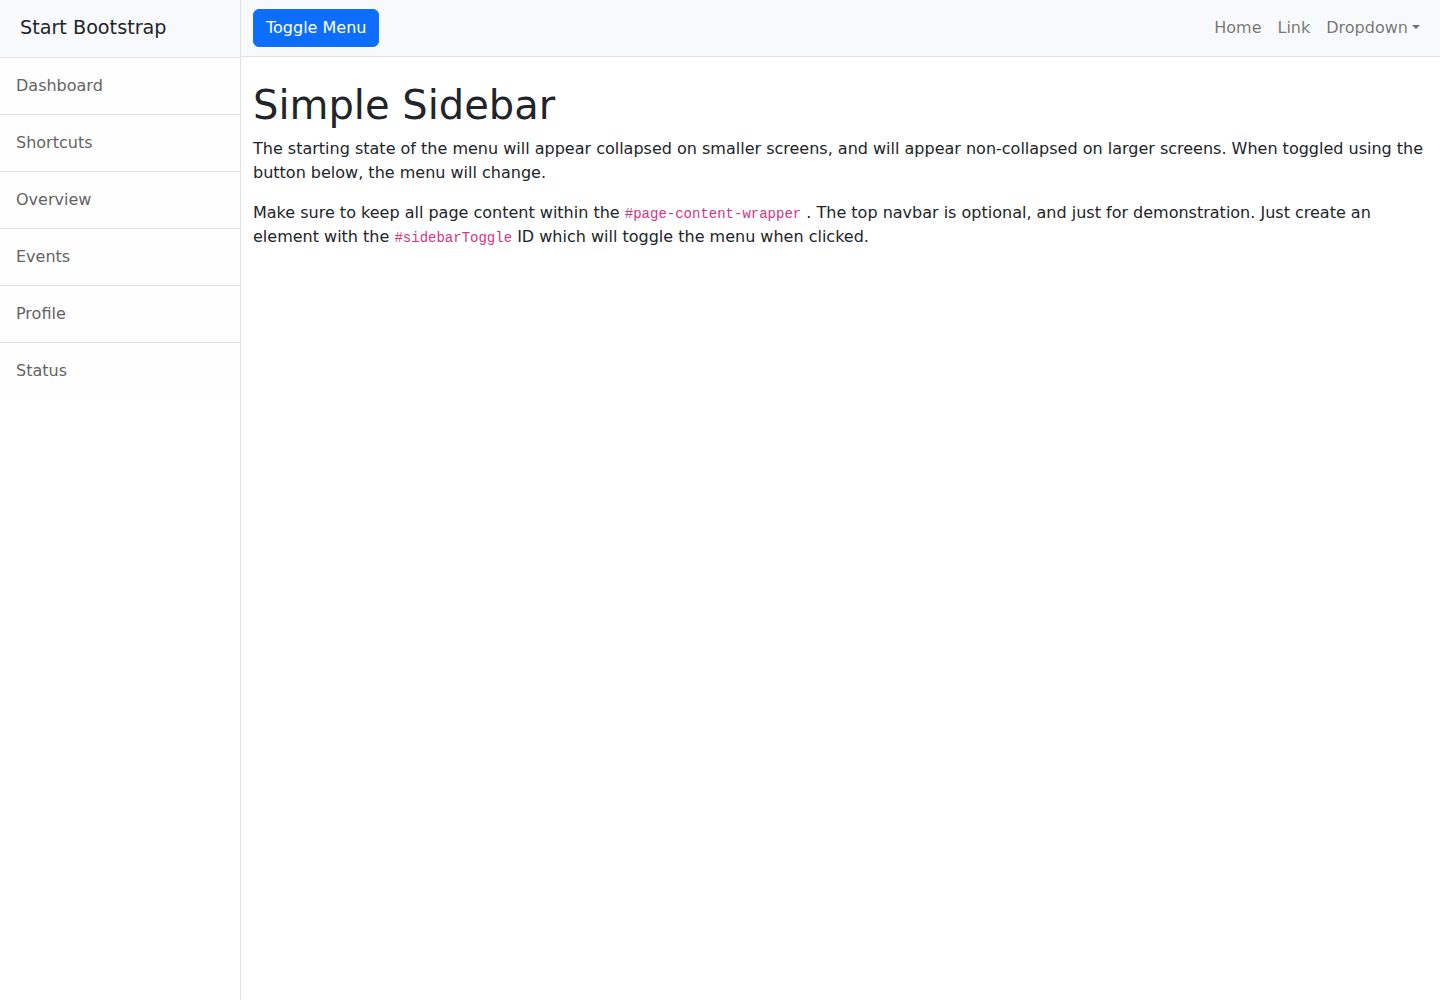
startbootstrap-simple-sidebar
A Bootstrap off-canvas sidebar navigation HTML starter template from Start Bootstrap. It provides directly editable HTML and CSS in the dist directory, while the source uses Pug, SCSS, and JavaScript with npm build scripts for live preview and compilation.
HTML · Starter
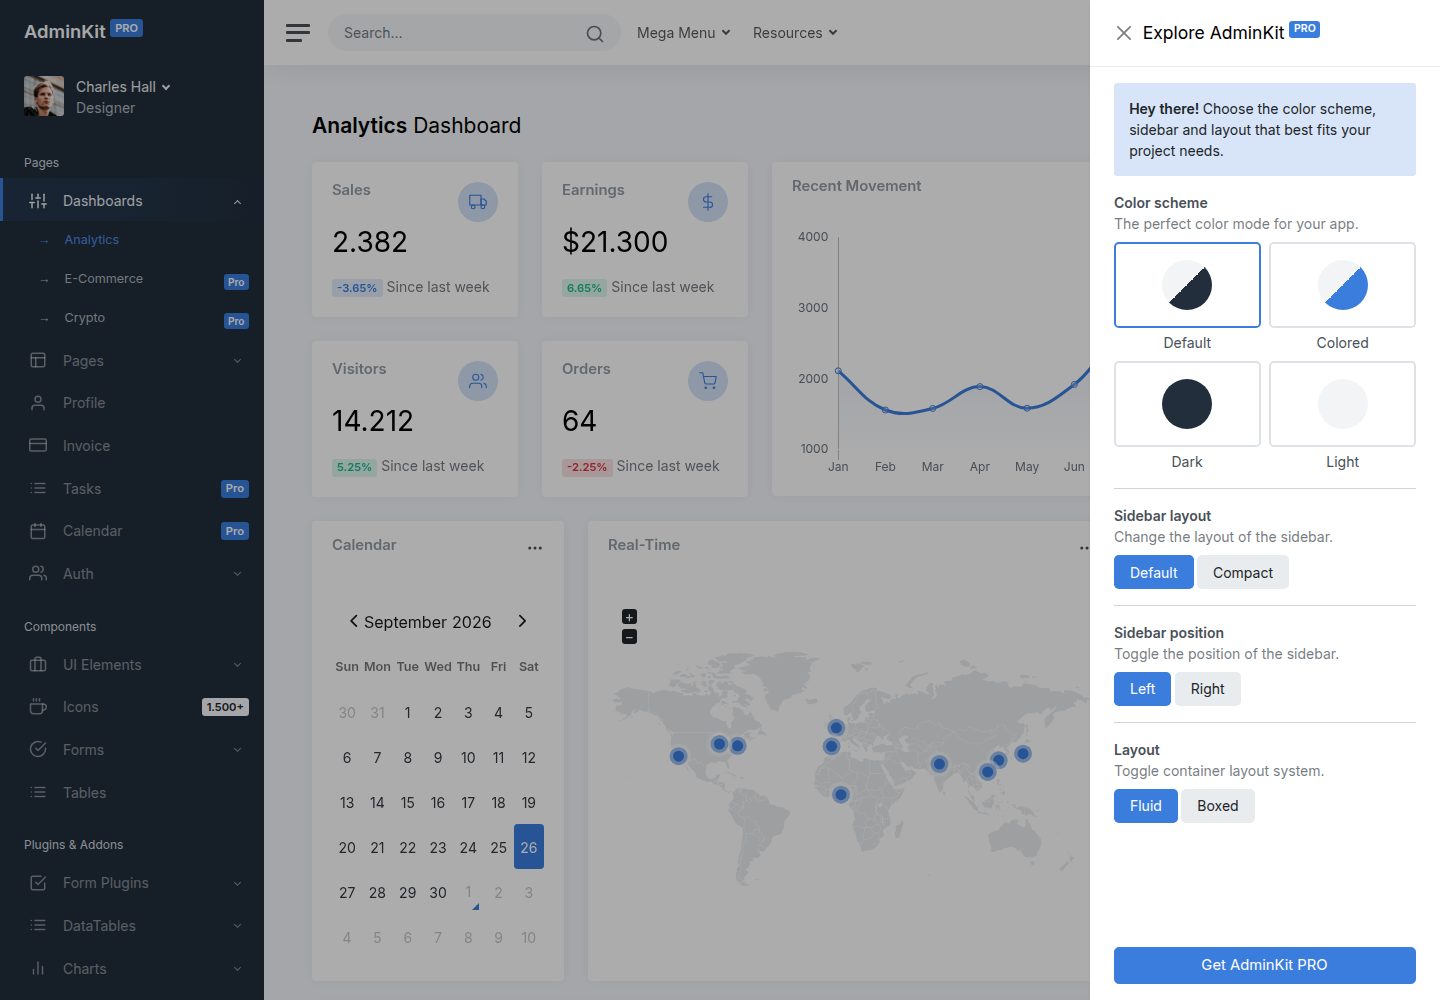
adminkit
AdminKit is a free, MIT-licensed HTML admin and dashboard template built on Bootstrap 5. The free version includes 15 demo pages, 1 plugin, and 1 color scheme, with hundreds of UI components, forms, tables, charts, and icons.
HTML · Admin dashboard
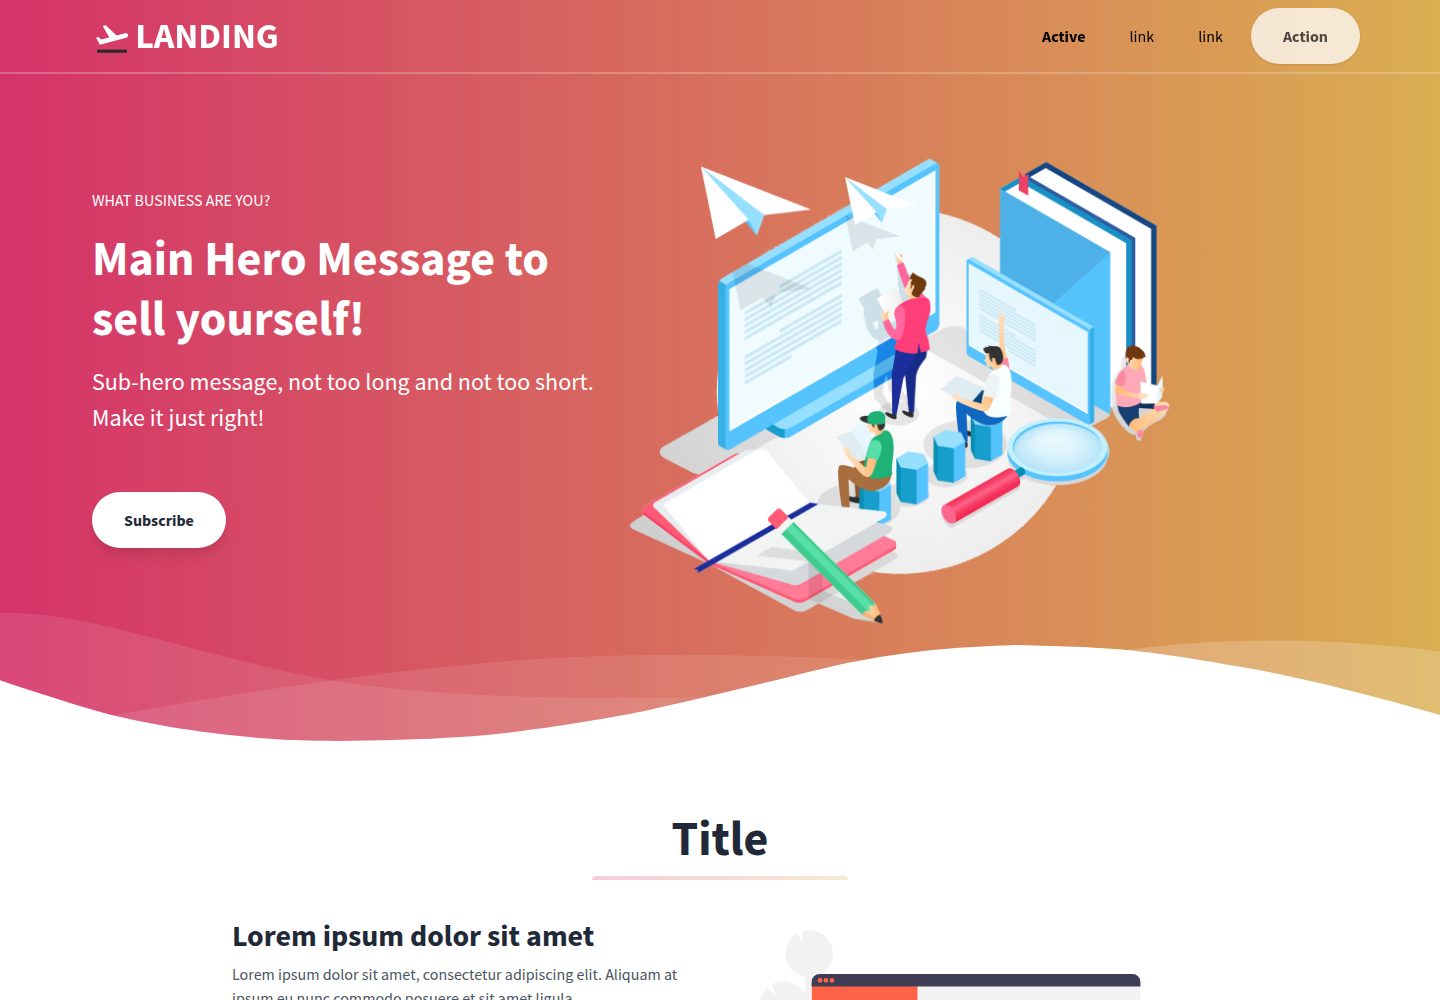
Landing-Page
A general-purpose landing page HTML template maintained by Tailwind Toolbox, written in pure HTML and loading the complete Tailwind CSS via CDN.
HTML · Corporate Website
light-bootstrap-dashboard
Light Bootstrap Dashboard is a free, MIT-licensed admin dashboard template from Creative Tim, built on Bootstrap with a responsive static HTML structure.
HTML · Admin dashboard
sing-app
Sing App Lite is a free, open-source admin dashboard template from Flatlogic, built with Bootstrap 4.5 and SCSS. It provides a responsive layout, dashboard examples, typography, tables, notifications, basic charts, icons, maps, and a hover sidebar, along with styled Bootstrap components.
HTML · Admin dashboard
startbootstrap-modern-business
Modern Business is a multipurpose Bootstrap full-site HTML template from Start Bootstrap with 17 standalone pages covering home, about, services, portfolio, pricing, blog, FAQ, and contact.
HTML · Starter