多租户数据隔离:查询按 organizationId 限定,不单独依赖路由参数
Next.jsReactSaaS启动器
TenantKit-Lite — Next.js SaaS模板
作者 Thaelith
TenantKit-Lite 是一个基于 Next.js 的多租户 SaaS 启动器,使用 Prisma 与 SQLite,内置 RBAC、邀请流程、审计日志、Vitest 单元测试和 GitHub Actions CI。
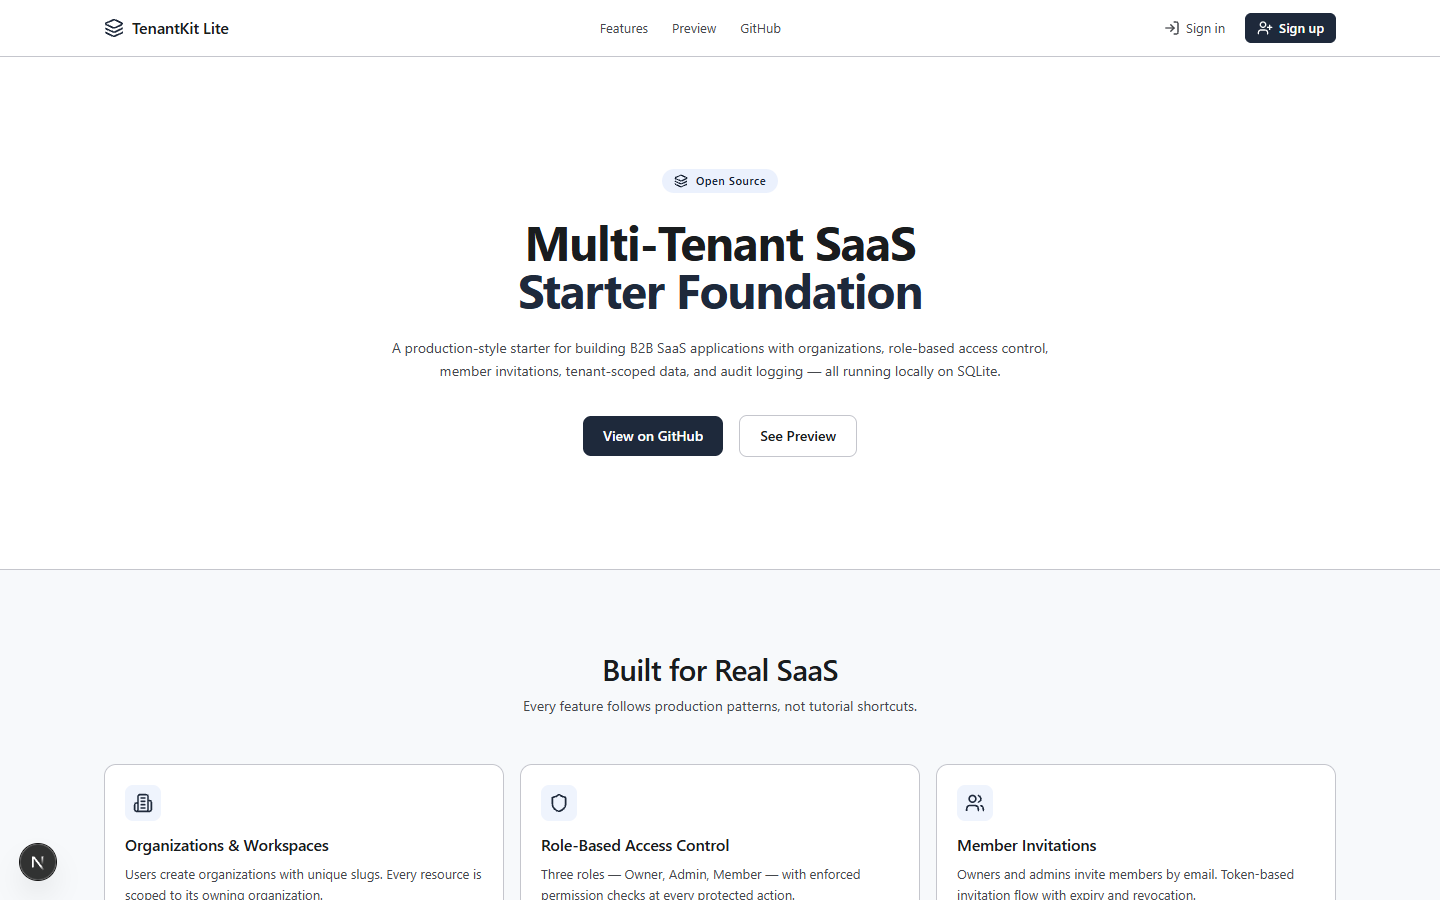
看看你的网站会是什么样
浏览真实页面截图,比较内容排版与手机效果。点击下方缩略图切换,放大查看整页细节。
目前有 1 张原始预览,可打开完整图片查看设计细节。
截图用于了解视觉与布局,交互效果请以实际项目为准。
采集于 2026-10-03查看来源
值得关注的模板亮点
从已有项目资料中,快速了解它的特点。
RBAC 角色模型:OWNER、ADMIN、MEMBER 三级权限在服务端校验
基于令牌的成员邀请流程,含注册引导与邀请消耗
审计日志记录操作者、动作、实体与 JSON 元数据
使用 Vitest 覆盖租户隔离、角色边界、令牌过期等逻辑
GitHub Actions 在推送和 PR 时执行 lint、类型检查、构建与测试
模板详细介绍
TenantKit-Lite 是一个面向 B2B SaaS 场景的多租户启动器,目标是在本地开发环境里演示企业级基础能力,而不依赖 Docker 或 PostgreSQL。它使用文件型 SQLite 数据库,克隆后即可运行。
项目围绕六个核心模型组织数据:User、Organization、Membership、Invitation、Project 和 AuditLog。认证采用 Auth.js(NextAuth v4)的邮箱/密码方式,密码经 bcryptjs 哈希;注册后自动创建默认组织并赋予 OWNER 角色。受保护资源在查询层按 organizationId 严格限定,避免仅依赖路由参数导致的越权访问。角色分为 OWNER、ADMIN 和 MEMBER,权限在服务端校验。邀请流程通过带过期时间的令牌生成链接,被邀请人注册或登录后建立 Membership 并消耗邀请。审计日志记录 actorId、action、entityId 及 JSON 元数据,用于查看组织内关键操作历史。
技术栈包括 Next.js App Router、TypeScript、Tailwind CSS、Prisma、SQLite、Auth.js、Zod、Lucide React 和 Vitest。测试集中在租户隔离、角色边界、令牌过期和审计集成等业务逻辑,GitHub Actions 在推送和拉取请求时执行 lint、类型检查、构建和单元测试。仓库提供 seed 脚本生成演示数据,并附带演示脚本与手动 QA 清单文档。
限制方面:项目定位为演示与作品集用途,README 未声明生产部署方案;SQLite 适合本地开发,切换生产数据库需要自行调整 Prisma 配置;外部服务(域名、托管、数据库、支付或 AI)可能产生额外费用;演示图片、字体、图标等第三方素材需单独核对许可。
Next.jsSaaS启动器
适合你的项目吗?
适用场景
- 学习 Next.js App Router 与 Server Actions 在多租户场景下的组织方式
- 在本地快速搭建带 RBAC 与邀请流程的 SaaS 原型
- 参考查询层租户隔离的写法,避免 IDOR 类越权问题
- 为组织内关键操作增加可追溯的审计日志
- 作为作品集项目展示认证、权限与测试的集成方式
适合人群
- 需要本地零依赖数据库快速启动多租户项目的开发者
- 希望参考 RBAC 与邀请流程实现细节的 Next.js 开发者
- 准备构建 B2B SaaS 原型并需要审计日志基础的个人或小团队
上手与定制指南
结合仓库当前版本的说明,按下面的资料检查内容、配置与运行要求。
- 1
需要 Node.js 20.9+ 与 npm 9+
- 2
复制 .env.example 为 .env,并生成 NEXTAUTH_SECRET
- 3
执行 npx prisma migrate dev --name init 初始化 SQLite 数据库
- 4
运行 npm run seed 可生成演示用户、项目与审计日志,演示密码为 demo123
- 5
若 seed 或删除本地数据库后出现会话异常,清除 localhost cookie 或退出登录后重新登录
授权与来源资料
使用条件与限制
免费使用 · 保留许可声明本次收录的是公开仓库中采用 MIT 许可的免费版本;免费范围为该版本代码,不代表外部服务或第三方素材免费。
使用时需要遵守
- 允许免费使用、修改、商用和分发该版本代码。
- 分发代码副本或实质性部分时,保留原作者版权声明和完整 MIT 许可声明。
- 代码按现状提供;担保与责任限制以原许可证及适用法律为准。
额外费用与待核对事项
- 演示图片、字体、图标及其他第三方素材需按各自许可核对,不能仅凭代码的 MIT 许可判断。
- 域名、托管、数据库、支付或 AI 等外部服务可能另外收费。
- 项目使用文件型 SQLite 数据库,便于本地克隆运行与学习,无需 Docker 或 PostgreSQL;生产环境若需其他数据库需自行调整 Prisma 配置。
- 该仓库定位为作品集展示项目,README 未声明生产部署方案或生产可用性保证。
- 演示账号密码统一为 demo123,仅用于本地演示数据,不应作为真实环境凭据使用。
- 运行 seed 或手动删除本地数据库后,浏览器可能残留已不存在用户的会话 cookie,导致“No organization access”或循环行为,需退出登录或清除 localhost cookie 后重新登录。
- 必须自行提供 NEXTAUTH_SECRET 环境变量,否则认证无法正常工作。
- 本地运行需要 Node.js 20.9+ 与 npm 9+ 环境。
查看原文依据
Permission is hereby granted, free of charge
许可证原文
It uses a file-based SQLite database so developers can clone, run, and learn without needing Docker or PostgreSQL.
README 原文
This repository serves as a portfolio piece showcasing:
README 原文
**Demo Credentials (all passwords are `demo123`):**
README 原文
If running `npm run seed` or manually deleting the local database causes a "No organization access" or loop behavior, it means your browser has a stale session cookie for a user that no longer exists in the database.
README 原文
| `NEXTAUTH_SECRET` | Auth.js JWT encryption secret | *(must be provided)* |
README 原文
https://github.com/Thaelith/TenantKit-Lite/blob/main/LICENSEhttps://github.com/Thaelith/TenantKit-Lite/blob/main/README.md- Node.js 20.9+ (Recommended for Next.js 15)
README 原文
DeepSeek 根据仓库许可证和 README 整理 ·2026-10-04。结果仅覆盖已读取资料,依赖、图片、字体及后续条款变更以各自原文为准。
项目核对记录与介绍依据
模板资料
- 来源平台
- GitHub
- 资料与维护参考分
- 资料一般 · 73 / 100
- 技术栈
- Next.js · React
- 网站类型
- SaaS · 启动器
这个分数如何计算
本站按许可资料(最高30分)、演示链接(12分)、预览图(10分)、Star数(15分)、记录的维护时间(15分)、描述完整度(8分)、功能记录(5分)和分类资料(5分)计算。它不是代码、安全或性能测试,也不是 Google 评分;有链接不代表已实测可用。
这个项目需要核对什么
- 记录的仓库更新时间
- 2026-04-27
- 截图检查日期
- 2026-10-04
目前没有记录演示链接。请依据仓库说明在本地评估;仅凭截图无法确认交互行为。
目录记录的主要技术栈是 Next.js。请通过依赖清单和锁文件核对实际版本与托管要求。这些说明基于收录资料,不代表代码审计或部署实测。
查看具体选型方法 →介绍的制作与核对状态
介绍由 AI 辅助整理目录与仓库资料。仓库作者不等于这篇介绍的审核者。
审核声明: [email protected] · 2026-10-04
查看当时使用的来源资料
SHA-256: d2749028979cf8151a9392275237d2d2eaa32be21ca7021544fd4e0d8dc3c591
2026-10-04T07:36:37.927Z
来源文件 / 仓库# TenantKit Lite [](https://github.com/Thaelith/TenantKit-Lite/actions)     A production-style multi-tenant SaaS starter built with Next.js, TypeScript, SQLite, Prisma, and robust Role-Based Access Control (RBAC). ## Why This Project Exists Many Next.js starter kits provide basic CRUD functionality but fail to address the complex requirements of true B2B SaaS applications. TenantKit Lite was built to demonstrate how to implement fundamental enterprise features—like hard tenant isolation, strict role-based access control, invitation workflows, and immutable audit logging—while keeping local development incredibly simple. It uses a file-based SQLite database so developers can clone, run, and learn without needing Docker or PostgreSQL. ## What This Demonstrates This repository serves as a portfolio piece showcasing: - **Security-First Design:** Structurally preventing Insecure Direct Object Reference (IDOR) attacks through query-level tenant isolation. - **Enterprise Capabilities:** Real-world implementations of RBAC and Audit Logging. - **Modern React Patterns:** Extensive use of Next.js App Router, Server Components, and Server Actions. - **Clean Architecture:** Keeping business logic testable and separated from UI components. ## Features - **Email/Password Authentication** — Register and login securely with bcryptjs password hashing via Auth.js. - **Auto-Workspace Creation** — New sign-ups automatically receive a default organization and the `OWNER` role. - **Multi-Tenant Architecture** — Isolated organizations and workspaces with unique slugs. - **Role-Based Access Control (RBAC)** — Strictly enforced `OWNER`, `ADMIN`, and `MEMBER` roles. - **Member Invitations** — Secure token-based invitation flow to add new members to workspaces. - **Tenant-Scoped Resources** — Queries are strictly scoped by `organizationId` to prevent cross-tenant data leaks. - **Audit Logging** — Automatic tracking of organization events (actor, action, entity, metadata). - **SQLite + Prisma** — Zero-dependency local database for instant setup. - **Fully Tested** — Unit tests cover critical security, isolation, and RBAC logic using Vitest. - **Automated CI** — GitHub Actions workflow ensures lint, build, and tests pass on every pull request. ## Demo & Seed Data You can quickly populate the database with realistic demo data, including users with different roles, projects, and audit logs. ```bash npm run seed ``` **Demo Credentials (all passwords are `demo123`):** - Owner: `[email protected]` (Full access) - Admin: `[email protected]` (Cannot access settings or delete org) - Member: `[email protected]` (Can only view/edit projects) > **Troubleshooting Note:** If running `npm run seed` or manually deleting the local database causes a "No organization access" or loop behavior, it means your browser has a stale session cookie for a user that no longer exists in the database. Simply click "Sign out" on the main landing page, or clear your localhost cookies, and log in with the new credentials. For a guided 5-minute walkthrough, see the [Demo Script](docs/demo-script.md). ## Screenshots ### Landing Page  ### Dashboard Overview  ### Projects  ### Members  ### Audit Logs  ## Tech Stack | Technology | Purpose | |---|---| | [Next.js 15](https://nextjs.org) | App Router, server components, API routes | | [TypeScript](https://www.typescriptlang.org) | Type safety and autocompletion | | [Tailwind CSS](https://tailwindcss.com) | Utility-first, responsive styling | | [Prisma](https://www.prisma.io) | ORM with strongly-typed queries | | [SQLite](https://www.sqlite.org) | Local-first, file-based database | | [Auth.js](https://authjs.dev) | Authentication (NextAuth v4) | | [Zod](https://zod.dev) | Input and API schema validation | | [Lucide React](https://lucide.dev) | SVG icon library | | [Vitest](https://vitest.dev) | Blazing fast unit testing framework | ## Architecture Overview ```text Browser ↓ Next.js App Router (React Server Components) ↓ Auth.js Session (Validates User Token) ↓ Permission Layer (Role + Membership Checks) ↓ Prisma ORM (Tenant-Scoped Queries) ↓ SQLite (file:./dev.db) ``` ## Database Schema Overview ```text User ──┬── Account (OAuth providers) ├── Session (auth tokens) └── Membership (Roles: OWNER, ADMIN, MEMBER) │ Organization ──┬── Project ├── Invitation └── AuditLog ``` The schema is built around six core models: `User`, `Organization`, `Membership`, `Invitation`, `Project`, and `AuditLog`. ## Tenant Isolation Notes Every protected resource is strictly scoped by `organizationId`. Queries never rely on route parameters alone — they always verify the current user's membership and permissions in the target organization. ```ts // Bad — No tenant scope (Vulnerable to IDOR) await prisma.project.findUnique({ where: { id: projectId } }); // Good — Strictly scoped by organization await prisma.project.findFirst({ where: { id: projectId, organizationId }, }); ``` ## Invitation Workflow 1. An `OWNER` or `ADMIN` generates an invitation link in the dashboard. 2. An `Invitation` record is created in the database with a secure, expiring token. 3. The recipient opens the link (`/invite/[token]`). 4. If they do not have an account, they are prompted to register. 5. Upon acceptance, a `Membership` record is created linking them to the organization, and the invitation is consumed. ## Audit Logging Critical actions (creating projects, editing resources, inviting members) are tracked. Audit logs capture the `actorId` (who did it), the `action` (what they did), the `entityId` (what was affected), and any relevant JSON metadata. This provides a transparent history for organization administrators. ## Testing & CI TenantKit Lite prioritizes logic validation over brittle UI tests. Essential business logic covering tenant isolation, role barriers, token expirations, and audit integrations are heavily tested using Vitest. - **Run tests locally:** `npm test` or `npm run test:watch` - **Continuous Integration:** GitHub Actions automatically runs linting, type-checking, builds, and unit tests on pushes and pull requests to `main`. ## Local Setup ### Prerequisites - Node.js 20.9+ (Recommended for Next.js 15) - npm 9+ ### Installation ```bash # Clone the repository git clone https://github.com/Thaelith/TenantKit-Lite.git cd TenantKit-Lite # Install dependencies npm install # Copy environment variables cp .env.example .env # Generate a secure NEXTAUTH_SECRET (or use the default for dev) node -e "console.log(require('crypto').randomBytes(32).toString('hex'))" # Run Prisma migrations to initialize the SQLite database npx prisma migrate dev --name init # Start the development server npm run dev ``` Open [http://localhost:3000](http://localhost:3000) to see the application. ## Environment Variables | Variable | Description | Default | |---|---|---| | `DATABASE_URL` | SQLite database file path | `file:./dev.db` | | `NEXTAUTH_SECRET` | Auth.js JWT encryption secret | *(must be provided)* | | `NEXTAUTH_URL` | Application base URL | `http://localhost:3000` | ## Manual QA Checklist Before deploying or finalizing major features, refer to the [Manual QA Checklist](docs/manual-qa.md) located in the `docs/` folder to verify system integrity. ## Roadmap | Phase | Milestone | Status | |---|---|---| | 1 | Project foundation, Prisma schema, landing page | Complete | | 2 | Authentication (Auth.js, login, register, auto-workspace) | Complete | | 3 | Organization dashboard, settings, members | Complete | | 4 | Tenant-scoped project CRUD | Complete | | 5 | Role-based access control enforcement | Complete | | 6 | Member invitation workflow | Complete | | 7 | Audit logging | Complete | | 8 | Testing (Vitest, validation logic) | Complete | | 9 | CI & GitHub portfolio polish | Complete | | 10 | Portfolio readiness, seed data, screenshots, docs | Complete | ## Security Please see [SECURITY.md](SECURITY.md) for vulnerability reporting and architecture principles. ## Contributing Please see [CONTRIBUTING.md](CONTRIBUTING.md) for guidelines on how to contribute. ## License [MIT License](LICENSE)
看看同类模板
对比同技术栈与用途的模板,找到更适合的视觉与内容结构。
ai-website-cloner-template
Clone any website with one command using AI coding agents
Next.js · 启动器

Next.js SaaS Starter
Next.js SaaS Starter 是 Next.js 官方维护的 SaaS 起点模板,定位介于学习资源和可直接部署的脚手架之间。
Next.js · SaaS

Next.js Commerce
Next.js Commerce 是 Vercel 团队维护的电商启动模板,基于 Next.js App Router 构建,采用服务端渲染、React Server Components、Server Actions …
Next.js · 电商

Next-js-Boilerplate
Next-js-Boilerplate 是一个面向 Next.js 16、Tailwind CSS 4 和 TypeScript 的启动器,核心定位是开发者体验优先。
Next.js · 启动器

tailwind-nextjs-starter-blog
tailwind-nextjs-starter-blog 是一个面向个人技术博客的 Next.js 与 Tailwind CSS 启动模板,其 v2 版本基于 App Router 与 React Server Comp…
Next.js · 博客

next-forge
Production-grade Turborepo template for Next.js apps.
Next.js · 启动器