基于 Next.js 14 App Router 组织目录结构
Next.jsReact后台启动器
nextjs14-supabase-dashboard — Next.js 后台模板
作者 w3labkr
基于 Next.js 14 与 Supabase 的后台仪表盘启动模板,集成 Prisma、Tailwind CSS、Shadcn 等依赖,提供认证、API 与状态管理的目录骨架。
看看你的网站会是什么样
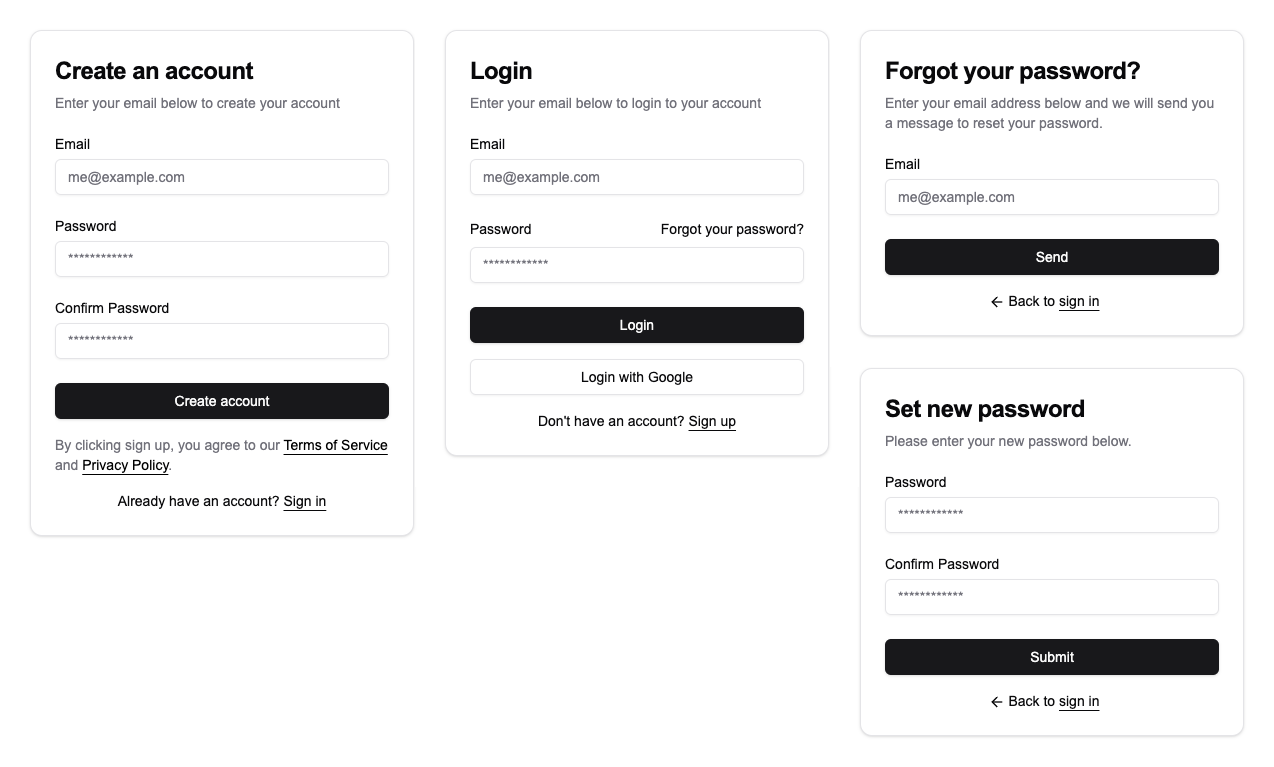
浏览真实页面截图,比较内容排版与手机效果。点击下方缩略图切换,放大查看整页细节。
目前有 1 张原始预览,可打开完整图片查看设计细节。
截图用于了解视觉与布局,交互效果请以实际项目为准。
采集于 2026-10-03查看来源
值得关注的模板亮点
从已有项目资料中,快速了解它的特点。
数据与认证层使用 Supabase,并通过 Supabase CLI 管理
使用 Prisma 管理数据库 Schema 与迁移
集成 Tailwind CSS 与 Shadcn 构建界面
内置 Zustand 状态管理与 React Query 数据请求
提供 auth 与 v1 两类 API 路由及 Server Actions 目录
模板详细介绍
这是一个面向 Next.js 14 的后台仪表盘启动模板,数据层基于 Supabase。README 说明其定位为 dashboard starter,仓库附带截图与依赖清单,采用 MIT 许可发布。
模板按 Next.js App Router 的项目结构组织目录,包含 actions(Server Actions)、app/api(auth 认证与 v1 公共 API)、components、config、context、hooks、lib、prisma、queries、schemas、store、supabase、types 等目录,public 下按 locales 划分国际化资源。依赖清单列出 Next.js 14、Tailwind CSS、Shadcn、Supabase Auth 与 Supabase CLI、Prisma、Zustand、React Query、Jose、Nodemailer、Browserslist、dayjs、qs、cookies-next。
使用流程为:克隆仓库、npm install、复制 .env.example 为 .env、执行 npx prisma migrate dev --name init 生成并运行 SQL 迁移、npm run dev 启动开发服务器。docs 目录下另有 DEPENDENCIES、GIT、PRISMA、SUPABASE 四份文档。README 还专门说明 Server Actions 的 CSRF 处理方式:Server Actions 仅接受 POST,Next.js 14 会比较 Origin 与 Host 头,不匹配则拒绝;由于不使用 CSRF token,HTML 净化很关键;若改用自定义 Route Handler(route.tsx),需自行实现 CSRF 防护。
限制方面:模板仅提供代码骨架与依赖组合,README 未给出功能完成度、测试覆盖或部署说明;Supabase、邮件等外部服务需自行配置,其可用性与费用不在代码许可范围内。
Next.jsReact后台启动器
适合你的项目吗?
适用场景
- 搭建带认证的后台仪表盘项目骨架
- 以 Supabase 作为后端数据与登录方案启动新项目
- 在 Next.js App Router 下组织 Server Actions 与 API 路由
- 使用 Prisma 迁移管理数据库结构的后台项目
适合人群
- 需要 Next.js 后台仪表盘起点的开发者
- 使用 Supabase 与 Prisma 的团队
- 偏好 Tailwind CSS 与 Shadcn 组件风格的项目
- 希望参考 App Router 目录组织方式的前端工程师
上手与定制指南
结合仓库当前版本的说明,按下面的资料检查内容、配置与运行要求。
- 1
克隆仓库后执行 npm install 安装依赖
- 2
将 .env.example 复制为 .env 并填写配置
- 3
执行 npx prisma migrate dev --name init 创建并运行迁移
- 4
运行 npm run dev 启动开发服务器
- 5
使用自定义 Route Handler 时需自行处理 CSRF 防护
授权与来源资料
使用条件与限制
免费使用 · 保留许可声明本次收录的是公开仓库中采用 MIT 许可的免费版本;免费范围为该版本代码,不代表外部服务或第三方素材免费。
使用时需要遵守
- 允许免费使用、修改、商用和分发该版本代码。
- 分发代码副本或实质性部分时,保留原作者版权声明和完整 MIT 许可声明。
- 代码按现状提供;担保与责任限制以原许可证及适用法律为准。
额外费用与待核对事项
- 模板依赖 Supabase 作为认证与数据后端,使用前需自行注册 Supabase 账号并配置项目,其服务可用性与费用由 Supabase 决定,不在 MIT 代码许可范围内。
- 运行前必须复制 .env.example 为 .env 并填写环境变量(如数据库连接、邮件等外部服务凭据),否则无法正常启动。
- 需执行 npx prisma migrate dev --name init 创建并运行数据库迁移,依赖可用的数据库连接,属于额外环境要求。
- 使用 Server Actions 时不含 CSRF token,需自行进行 HTML 净化;若改用自定义 Route Handler(route.tsx),必须手动实现 CSRF 防护。
- 演示图片、字体、图标及其他第三方素材需按各自许可核对,不能仅凭代码的 MIT 许可判断。
- 域名、托管、数据库、支付或 AI 等外部服务可能另外收费。
查看原文依据
Permission is hereby granted, free of charge
许可证原文
Supabase Auth + Supabase CLI
README 原文
Copy of the `.env.example` if the `.env` doesn't exist.
README 原文
Create an SQL migration file and execute it.
README 原文
https://github.com/w3labkr/nextjs14-supabase-dashboard/blob/master/LICENSEhttps://github.com/w3labkr/nextjs14-supabase-dashboard/blob/master/README.mdServer Actions doesn't use CSRF tokens, therefore HTML sanitization is crucial.
README 原文
DeepSeek 根据仓库许可证和 README 整理 ·2026-10-03。结果仅覆盖已读取资料,依赖、图片、字体及后续条款变更以各自原文为准。
项目核对记录与介绍依据
模板资料
- 来源平台
- GitHub
- 资料与维护参考分
- 资料一般 · 70 / 100
- 技术栈
- Next.js · React
- 网站类型
- 后台 · 启动器
这个分数如何计算
本站按许可资料(最高30分)、演示链接(12分)、预览图(10分)、Star数(15分)、记录的维护时间(15分)、描述完整度(8分)、功能记录(5分)和分类资料(5分)计算。它不是代码、安全或性能测试,也不是 Google 评分;有链接不代表已实测可用。
这个项目需要核对什么
- 记录的仓库更新时间
- 2025-02-16
- 截图检查日期
- 2026-10-03
目前没有记录演示链接。请依据仓库说明在本地评估;仅凭截图无法确认交互行为。
目录记录的主要技术栈是 Next.js。请通过依赖清单和锁文件核对实际版本与托管要求。这些说明基于收录资料,不代表代码审计或部署实测。
查看具体选型方法 →介绍的制作与核对状态
介绍由 AI 辅助整理目录与仓库资料。仓库作者不等于这篇介绍的审核者。
审核声明: [email protected] · 2026-10-04
查看当时使用的来源资料
SHA-256: 582d023eb0149148667072c75de4fe9c76e51691fd15d61ffec77f20cfdfe8b7
2026-10-03T23:18:55.978Z
来源文件 / 仓库# nextjs14-supabase-dashboard This is a dashboard starter template for the [NextJS](https://nextjs.org) 14 based on [Supabase](https://supabase.com). ## Screenshots  ## Denpendencies - Next.js 14 - Tailwindcss - Shadcn - Supabase Auth + Supabase CLI - Prisma - Zustand - React Query - Jose - Nodemailer - Browserslist - dayjs - qs - cookies-next ## Folder and file Structure The folder and file structure is based on nextjs app router [next.js project structure](https://nextjs.org/docs/getting-started/project-structure). ```txt . ├── actions/ # Server Actions ├── app/ # App Router │ └── api/ │ ├── auth/ # Authentication │ └── v1/ # Public APIs ├── components/ # React components ├── config/ # Configuration for site ├── context/ # Context ├── docs/ # Documents ├── hooks/ # Hooks ├── lib/ # Application specific libraries & Utility functions ├── prisma/ # Prisma Schema Location and Configuration ├── public/ # Static assets to be served │ └── [locales]/ # Internationalization ├── queries/ # APIs ├── schemas/ # Schema validations ├── screenshots/ # Screenshots ├── store/ # State ├── supabase/ # Supabase CLI ├── types/ # Type definitions └── package.json ``` ## Getting Started Clone the repository to the current directory. ```shell git clone https://github.com/w3labkr/nextjs14-supabase-dashboard.git . ``` Install all modules listed as dependencies. ```shell npm install ``` Copy of the `.env.example` if the `.env` doesn't exist. ```shell cp .env.example .env ``` Create an SQL migration file and execute it. ```shell npx prisma migrate dev --name init ``` Start the development server. ```shell npm run dev ``` ## Documents - [DEPENDENCIES](./docs/DEPENDENCIES.md) - [GIT](./docs/GIT.md) - [PRISMA](./docs/PRISMA.md) - [SUPABASE](./docs/SUPABASE.md) ## CSRF > All Server Actions can be invoked by plain `<form>`, which could open them up to CSRF attacks. Behind the scenes, Server Actions are always implemented using POST and only this HTTP method is allowed to invoke them. This alone prevents most CSRF vulnerabilities in modern browsers, particularly due to Same-Site cookies being the default. > > As an additional protection Server Actions in Next.js 14 also compares the Origin header to the Host header (or X-Forwarded-Host). If they don't match, the Action will be rejected. In other words, Server Actions can only be invoked on the same host as the page that hosts it. Very old unsupported and outdated browsers that don't support the Origin header could be at risk. > > Server Actions doesn't use CSRF tokens, therefore HTML sanitization is crucial. > > When Custom Route Handlers (route.tsx) are used instead, extra auditing can be necessary since CSRF protection has to be done manually there. The traditional rules apply there. [How to Think About Security in Next.js](https://nextjs.org/blog/security-nextjs-server-components-actions) ## License This software license under the [MIT License](LICENSE).
看看同类模板
对比同技术栈与用途的模板,找到更适合的视觉与内容结构。
ai-website-cloner-template
Clone any website with one command using AI coding agents
Next.js · 启动器

Next.js SaaS Starter
Next.js SaaS Starter 是 Next.js 官方维护的 SaaS 起点模板,定位介于学习资源和可直接部署的脚手架之间。
Next.js · SaaS

Next.js Commerce
Next.js Commerce 是 Vercel 团队维护的电商启动模板,基于 Next.js App Router 构建,采用服务端渲染、React Server Components、Server Actions …
Next.js · 电商

Next-js-Boilerplate
Next-js-Boilerplate 是一个面向 Next.js 16、Tailwind CSS 4 和 TypeScript 的启动器,核心定位是开发者体验优先。
Next.js · 启动器

tailwind-nextjs-starter-blog
tailwind-nextjs-starter-blog 是一个面向个人技术博客的 Next.js 与 Tailwind CSS 启动模板,其 v2 版本基于 App Router 与 React Server Comp…
Next.js · 博客

next-forge
Production-grade Turborepo template for Next.js apps.
Next.js · 启动器