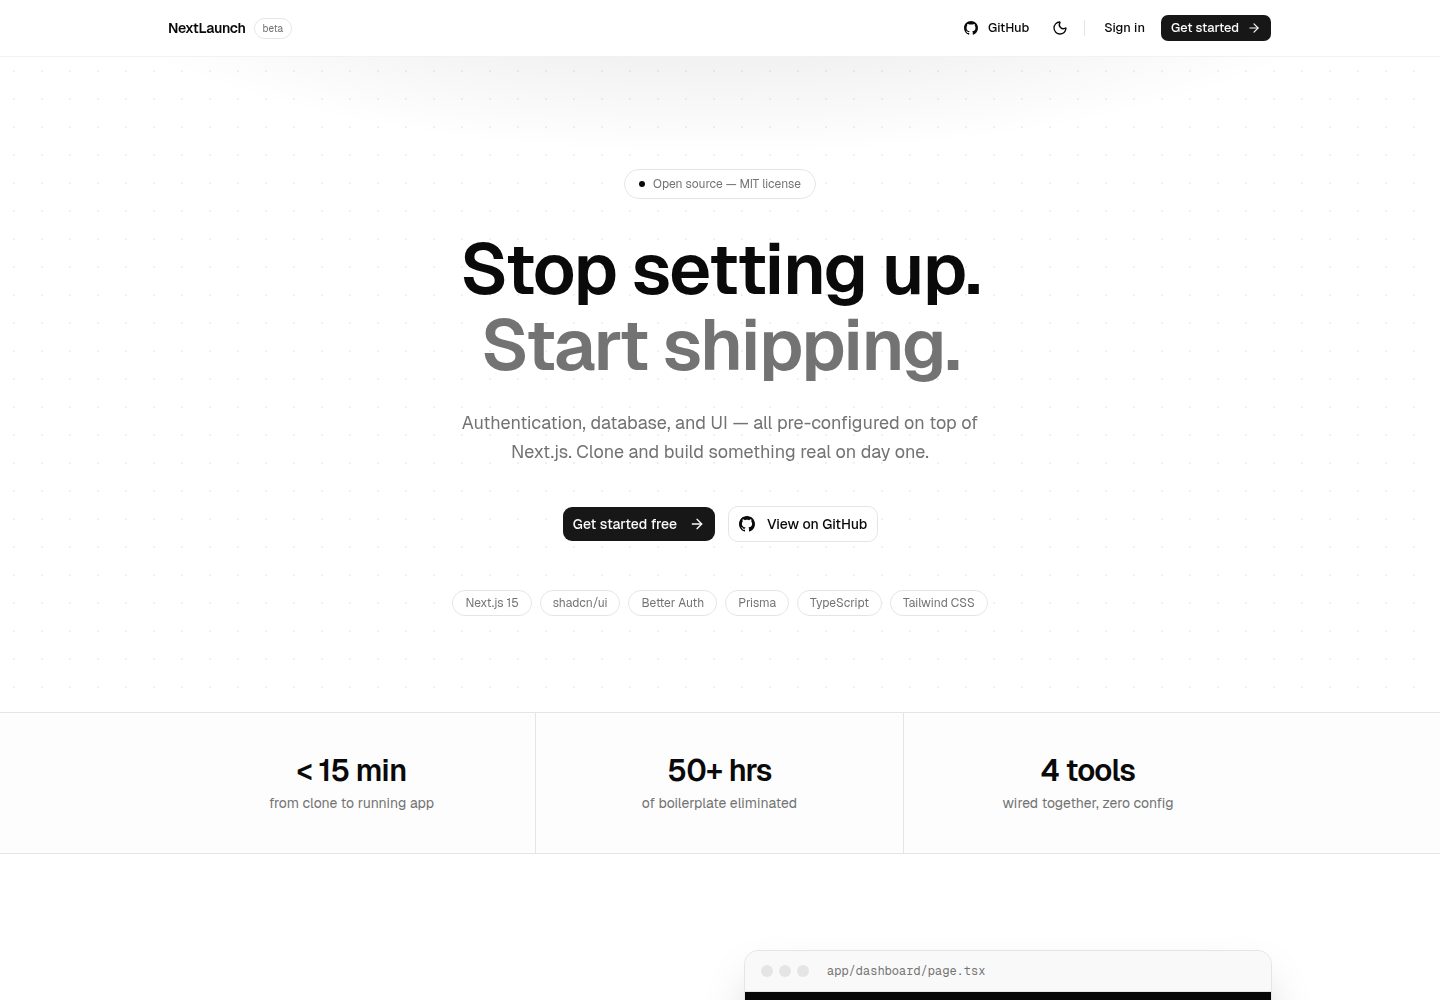
Preconfigured Better Auth authentication, supporting email-password registration and login, session management, Google and GitHub OAuth, and TOTP two-factor authentication
Next.jsReactSaaSStarter
next-launch — Next.js SaaS Template
By adityayaduvanshi
NextStack is a starter template based on Next.js 15 App Router, preconfigured with Better Auth authentication, Prisma 7 and PostgreSQL database, shadcn/ui component library, and Tailwind CSS v4, and provides email-password, OAuth, two-factor authentication, and protected routes configurations.
Explore the design
Compare the page layouts and mobile experience. Open any screenshot for a closer look.
Desktop homepage1 / 2
Desktop captureTop of page
Actual screenshot captured by the server browser.
All pages & views 2
Screenshots show visual appearance; interactive behavior may differ.
Recorded 2026-10-14View source
What stands out
A quick read of the recorded project description.
Uses Prisma 7 with PostgreSQL, providing a type-safe database client and migration commands
Over 50 preinstalled shadcn/ui components, paired with Tailwind CSS v4 and the Geist font
Protected routes implemented via middleware, with login and registration pages reusable through a single AuthPage component
Light and dark theme switching using next-themes
Project name, description, and URL are configured in one place in config/app.ts
Template Details
This template is aimed at developers who need to quickly build a Next.js application with authentication and a database. The README states its tech stack includes Next.js 15 (App Router, Turbopack), TypeScript, Better Auth, Prisma 7 (PostgreSQL), shadcn/ui, Tailwind CSS v4, and the Geist font. Functionally it provides email-password registration and login with session management, Google and GitHub OAuth that can be enabled via environment variables, TOTP-based two-factor authentication, middleware-based protected routes, a type-safe Prisma client, over 50 preinstalled shadcn/ui components, light and dark themes using next-themes, and login and registration templates driven by a single AuthPage component. Project configuration is centralized in config/app.ts for modifying the app name, description, and URL. The README does not provide information about performance, production readiness, or capabilities beyond the features above.
Next.jsSaaSlauncher
Is it right for your project?
Use Cases
- Quickly building a Next.js application with email-password, OAuth, and two-factor authentication
- Projects using Prisma and PostgreSQL as a type-safe database layer
- Interface development where the shadcn/ui component library and Tailwind CSS styles are directly reused
- Admin or user center applications requiring protected routes and session management
- Next.js applications deployed via Vercel or Docker
Suitable For
- Developers familiar with Next.js App Router and TypeScript
- Projects that need preconfigured authentication and database setup to shorten initial scaffolding time
- Teams planning to use PostgreSQL and Prisma for data modeling
- Developers who want to build custom interfaces based on shadcn/ui
Getting started & customization
Use these recorded setup notes alongside the repository instructions for your chosen version.
- 1
After cloning the repository, run npm install to install dependencies
- 2
Copy env.example to .env and fill in required variables such as NEXT_PUBLIC_APP_URL, BETTER_AUTH_SECRET, BETTER_AUTH_URL, and DATABASE_URL
- 3
Run npx prisma migrate dev --name init to push the database schema
- 4
Run npm run dev to start the development server, accessible by default at http://localhost:3000
- 5
OAuth providers are automatically enabled after configuring the corresponding client ID and secret in .env; the callback URL is /api/auth/callback/{provider}
License & source material
Usage conditions & limitations
Free to use · keep license noticeThis entry covers the free version under the MIT license in the public repository; the free scope is the code of this version and does not mean external services or third-party assets are free.
Must comply with when using
- Free use, modification, commercial use, and distribution of this version's code are permitted.
- When distributing copies or substantial portions of the code, retain the original author's copyright notice and the complete MIT license notice.
- The code is provided as is; warranties and limitations of liability are governed by the original license and applicable law.
Additional costs & items to verify
- Demo images, fonts, icons, and other third-party assets must be checked against their respective licenses and cannot be judged solely by the code's MIT license.
- External services such as domains, hosting, databases, payments, or AI may incur separate charges.
- A PostgreSQL database connection string (DATABASE_URL) must be provided; the project depends on an external PostgreSQL service to run.
- A random BETTER_AUTH_SECRET key must be generated and configured yourself, otherwise authentication will not work properly.
- Enabling Google OAuth requires applying for and configuring GOOGLE_CLIENT_ID and GOOGLE_CLIENT_SECRET yourself, which is an external service account requirement.
- Enabling GitHub OAuth requires applying for and configuring GITHUB_CLIENT_ID and GITHUB_CLIENT_SECRET yourself, which is an external service account requirement.
- Using OAuth requires setting the callback URL yourself in the corresponding provider's backend, which is an external service configuration requirement.
- When deploying to Vercel, all environment variables must be manually configured in the platform dashboard, including the URL corresponding to the production domain.
View Original Text Basis
Permission is hereby granted, free of charge
Original License Text
| `DATABASE_URL` | Yes | PostgreSQL connection string |
Original README
| `BETTER_AUTH_SECRET` | Yes | Random secret — run `openssl rand -base64 32` |
Original README
| `GOOGLE_CLIENT_ID` | Optional | Enables Google OAuth |
Original README
| `GITHUB_CLIENT_ID` | Optional | Enables GitHub OAuth |
Original README
2. Set the OAuth callback URL in your provider's dashboard:
Original README
https://github.com/adityayaduvanshi/next-launch/blob/master/LICENSEhttps://github.com/adityayaduvanshi/next-launch/blob/master/README.mdSet all environment variables in the Vercel dashboard under **Settings → Environment Variables**. Make sure `NEXT_PUBLIC_APP_URL` and `BETTER_AUTH_URL` are set to your production domain.
Original README
Compiled by DeepSeek based on repository license and README ·2026-10-14. Results only cover the materials read; dependencies, images, fonts, and subsequent term changes are subject to their respective original texts.
Project checks & description sources
Template Information
- Source platforms
- GitHub
- Documentation and maintenance reference score
- More documented · 80 / 100
- Technologies
- Next.js · React
- Website type
- SaaS · Starter
How this score is calculated
Our heuristic uses license records (up to 30), a demo link (12), a preview (10), stars (15), recorded maintenance (15), description completeness (8), feature records (5) and classification data (5). It is not a code, security or performance test, or a Google score. A link does not establish tested functionality.
What to verify for this project
- Repository update recorded
- 2026-04-12
- Screenshot last checked
- 2026-10-14
A demo link is listed. Check it with your own content and viewport sizes; its presence does not confirm that forms, authentication or payments work.
The catalog identifies Next.js as the primary stack. Check the actual dependency manifest and lockfile for versions and hosting requirements. These notes use recorded metadata, not a code audit or a deployment test.
Use a selection guide →How this description was prepared
AI-assisted description based on catalog records and repository material. Repository authors are not automatically the reviewers of this description.
Review declaration: codex-user-requested-batch-review-20261015 · 2026-10-15
Inspect the recorded source material
SHA-256: 24992ad20f8d7108f2a9e2c6485c8801fba12d405ea8bd08d3ced81ed157d9fa
2026-10-14T18:12:19.231Z
Source file / repository# NextStack
A production-ready Next.js starter with authentication, a type-safe database, and a complete UI system — all pre-configured so you can start building on day one.
## Stack
| Layer | Technology |
|---|---|
| Framework | [Next.js 15](https://nextjs.org) (App Router, Turbopack) |
| Language | [TypeScript](https://www.typescriptlang.org) |
| Auth | [Better Auth](https://better-auth.com) |
| Database ORM | [Prisma 7](https://www.prisma.io) (PostgreSQL) |
| UI Components | [shadcn/ui](https://ui.shadcn.com) |
| Styling | [Tailwind CSS v4](https://tailwindcss.com) |
| Fonts | [Geist](https://vercel.com/font) |
## Features
- **Email/password auth** — sign up, sign in, session management
- **OAuth** — Google and GitHub (enable by adding env vars)
- **Two-factor authentication** — TOTP-based 2FA via Better Auth plugin
- **Protected routes** — middleware-based route protection, ready to extend
- **Type-safe database** — Prisma client with full TypeScript inference
- **Component library** — 50+ shadcn/ui components pre-installed
- **Dark mode** — light/dark theme with `next-themes`
- **Reusable auth templates** — single `AuthPage` component drives both sign-in and sign-up
- **Project config** — one file (`config/app.ts`) to rename and rebrand everything
---
## Getting Started
### 1. Clone the repository
```bash
git clone https://github.com/adityayaduvanshi/next-launch.git
cd next-launch
```
### 2. Install dependencies
```bash
npm install
```
### 3. Set up environment variables
```bash
cp env.example .env
```
Then fill in your values (see [Environment Variables](#environment-variables) below).
### 4. Push the database schema
```bash
npx prisma migrate dev --name init
```
### 5. Start the dev server
```bash
npm run dev
```
Open [http://localhost:3000](http://localhost:3000).
---
## Environment Variables
| Variable | Required | Description |
|---|---|---|
| `NEXT_PUBLIC_APP_URL` | Yes | Your app's public URL (e.g. `http://localhost:3000`) |
| `BETTER_AUTH_SECRET` | Yes | Random secret — run `openssl rand -base64 32` |
| `BETTER_AUTH_URL` | Yes | Same as `NEXT_PUBLIC_APP_URL` |
| `DATABASE_URL` | Yes | PostgreSQL connection string |
| `GOOGLE_CLIENT_ID` | Optional | Enables Google OAuth |
| `GOOGLE_CLIENT_SECRET` | Optional | Enables Google OAuth |
| `GITHUB_CLIENT_ID` | Optional | Enables GitHub OAuth |
| `GITHUB_CLIENT_SECRET` | Optional | Enables GitHub OAuth |
> OAuth providers are **automatically disabled** if their env vars are not set — no code changes needed.
---
## Project Structure
```
next-app/
├── app/
│ ├── (auth)/ # Auth route group
│ │ ├── _components/
│ │ │ ├── auth-form.tsx # Shared sign-in / sign-up form
│ │ │ └── auth-page.tsx # Page shell with logic & layout
│ │ ├── sign-in/[[...sign-in]]/page.tsx
│ │ └── sign-up/[[...sign-up]]/page.tsx
│ ├── (marketing)/ # Public marketing pages
│ │ ├── _components/
│ │ │ └── theme-toggle.tsx
│ │ └── page.tsx # Landing page
│ ├── globals.css
│ └── layout.tsx # Root layout with metadata
├── config/
│ └── app.ts # ← Project name, description, URL
├── lib/
│ ├── auth/
│ │ ├── auth.ts # Better Auth server config
│ │ ├── auth-client.ts # Better Auth browser client
│ │ └── index.ts
│ ├── db.ts # Prisma client singleton
│ └── utils.ts
├── prisma/
│ └── schema.prisma # Database schema
├── components/
│ └── ui/ # shadcn/ui components
└── env.example
```
---
## Customization
### Rename the project
Edit `config/app.ts` — this is the single source of truth for your app's name, description, and URL:
```ts
export const appConfig = {
name: "YourApp",
description: "Your app description",
url: "https://yourapp.com",
}
```
### Add a database model
1. Add your model to `prisma/schema.prisma`
2. Run `npx prisma migrate dev --name your-model`
3. Use it anywhere via `import db from "@/lib/db"`
```ts
import db from "@/lib/db"
const posts = await db.post.findMany({
where: { authorId: session.user.id },
})
```
### Access the session in a Server Component
```ts
import { headers } from "next/headers"
import { auth } from "@/lib/auth"
export default async function Page() {
const session = await auth.api.getSession({
headers: await headers(),
})
if (!session) redirect("/sign-in")
return <div>Hello, {session.user.name}</div>
}
```
### Add an OAuth provider
1. Add credentials to `.env`:
```
GOOGLE_CLIENT_ID=your-client-id
GOOGLE_CLIENT_SECRET=your-client-secret
```
2. Set the OAuth callback URL in your provider's dashboard:
```
http://localhost:3000/api/auth/callback/google
```
That's it — the provider activates automatically.
### Enable / disable Two-Factor Auth
2FA is enabled by default via the `twoFactor()` plugin in `lib/auth/auth.ts`. Remove it from the `plugins` array to disable it.
---
## Available Scripts
```bash
npm run dev # Start dev server (Turbopack)
npm run build # Production build
npm run start # Start production server
npm run typecheck # TypeScript type check
npm run lint # ESLint
npm run format # Prettier
```
---
## Deployment
### Vercel (recommended)
```bash
npm i -g vercel
vercel
```
Set all environment variables in the Vercel dashboard under **Settings → Environment Variables**. Make sure `NEXT_PUBLIC_APP_URL` and `BETTER_AUTH_URL` are set to your production domain.
### Docker / other platforms
Build the production image:
```bash
npm run build
npm run start
```
The app runs on port `3000` by default.
---
## License
MIT — use this for anything, personal or commercial.
Explore similar templates
Compare previews and descriptions within the same stack and category.
Next.js SaaS Starter
The official Next.js SaaS starter template, integrating email/password authentication, Stripe Checkout subscriptions, a dashboard with user/team CRUD, basic Owner/Member RBAC, and activity logging.
Next.js · SaaS
Next.js Commerce
Vercel's officially maintained Next.js App Router ecommerce starter with deep Shopify integration, offering a complete product catalog, cart, and checkout flow. Core logic is modular for swapping backends, and community provider versions exist for BigCommerce, Medusa, and Saleor.
Next.js · E-commerce
Next-js-Boilerplate
A developer-first Next.js 16 starter with Tailwind CSS 4 and TypeScript, supporting both App Router and Page Router.
Next.js · Starter
tailwind-nextjs-starter-blog
A Next.js and Tailwind CSS blog starter template using Contentlayer for Markdown/MDX, with built-in SEO, code highlighting, and tags. It targets personal technical blogs and migration from Jekyll/Hugo to React, and supports one-click Vercel deployment.
Next.js · Blog
next-forge
next-forge is a Turborepo-based Next.js template maintained by Vercel, positioned as a starting point for SaaS products.
Next.js · Starter
SaaS-Boilerplate
SaaS-Boilerplate is an open-source SaaS starter template built with Next.js App Router, React 19, TypeScript, Tailwind CSS, and Shadcn UI.
Next.js · SaaS