Turborepo monorepo structure with an apps/playground playground and a packages/logger shared logging package
Next.jsViteReactStarter
agentic-monorepo-starter — Next.js Starter Template
By valuecodes
A Turborepo monorepo template for agent-assisted development, including a Vite playground, shared tooling, strict TypeScript configuration, CI checks, and Claude Code setup.
Explore the design
Compare the page layouts and mobile experience. Open any screenshot for a closer look.
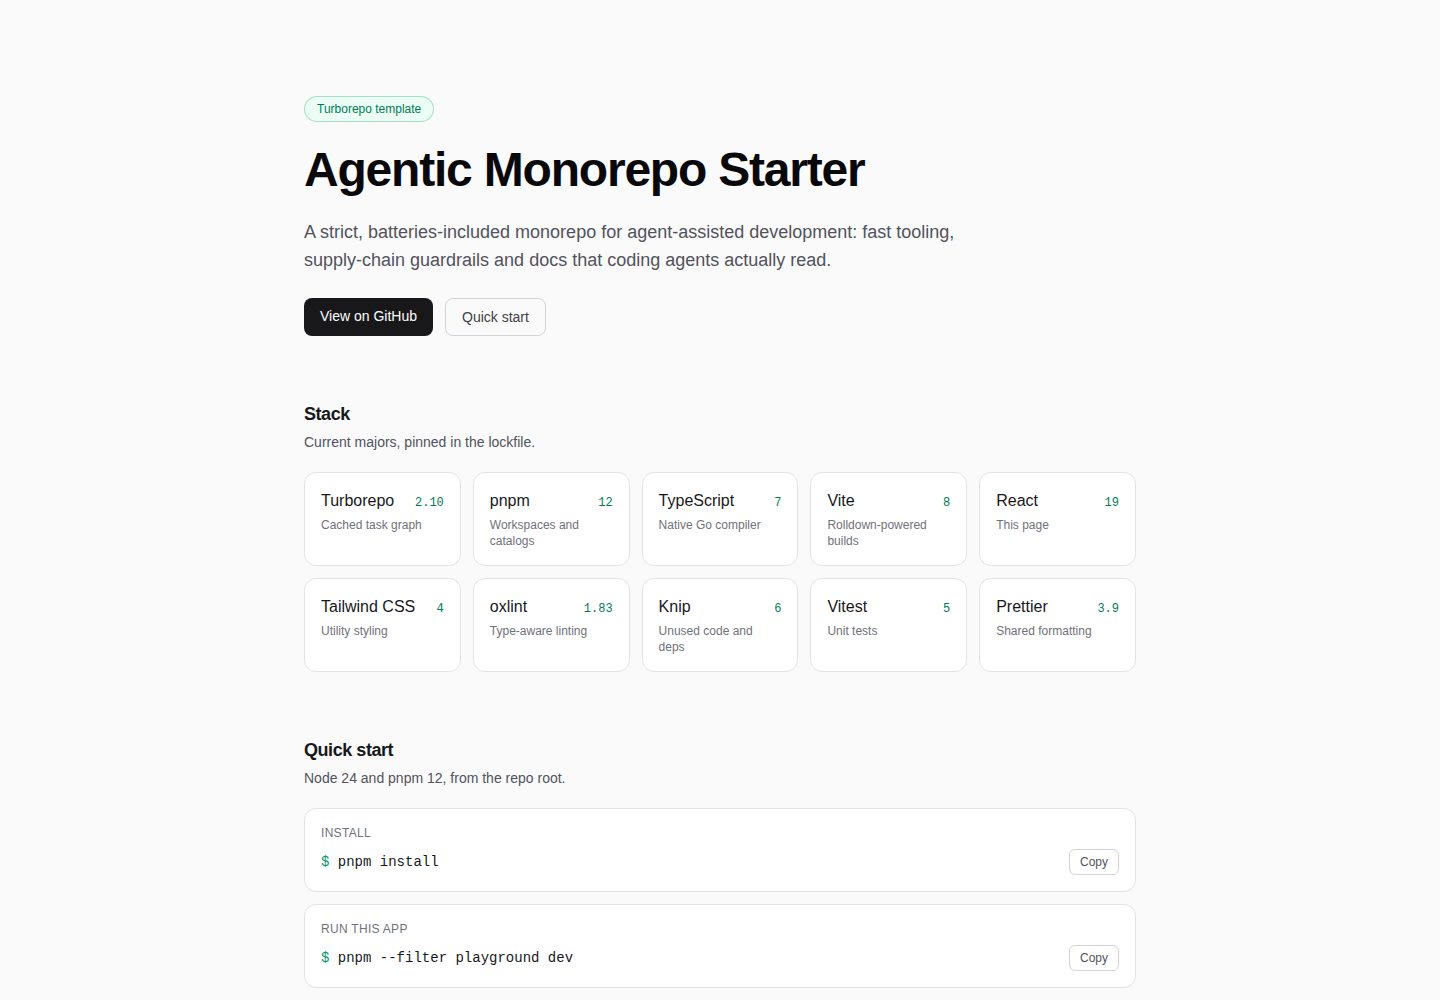
Desktop homepage1 / 2
Desktop captureTop of page
Actual screenshot captured by the server browser.
All pages & views 2
Screenshots show visual appearance; interactive behavior may differ.
Recorded 2026-10-09View source
What stands out
A quick read of the recorded project description.
Unified toolchain: oxlint, Knip, Prettier, TypeScript, and Turbo, with a single root lint configuration
pnpm catalog version management with supply-chain protections including a 14-day release wait, trust downgrade checks, and prohibition of git/tarball sub-dependencies
CI covers typecheck, lint, knip, format-check, test, build, gitleaks secret scanning, and CodeQL
Built-in Claude Code settings under .claude/, aimed at agent-assisted development
Template Details
This is a Turborepo-based monorepo starter template positioned for AI coding agents to work within a constrained repository structure. The repository provides a Vite playground app (apps/playground), a shared @repo/logger logging package, and shared configurations under the tooling directory for Prettier, TypeScript, and a GitHub composite action. The root uses a single oxlint configuration covering the entire repository and manages dependency versions through a pnpm catalog, while adding supply-chain protections: dependency releases must wait 14 days, trust downgrades are checked, and git/tarball sub-dependencies are prohibited. The repository also includes Claude Code settings under .claude/ and a gitleaks secret scanning script.
For usage, the template requires Node.js 24.21.0 and pnpm 12.6.0; after installation, pnpm dev starts the playground on port 3000. Commands cover lint, knip, typecheck, test, build, format, and secrets:scan; CI runs typecheck, lint, knip, format-check, test, build, and gitleaks scanning on pushes to main and pull requests, and also runs CodeQL code scanning.
Regarding limitations, CodeQL is free for public repositories, while private repositories require GitHub Code Security; if default setup is enabled under Settings → Code security, it must be disabled first, otherwise workflow uploads will be rejected. secrets:scan depends on gitleaks v8.19+ in PATH or a running Docker. The repository deliberately does not provide .github/dependabot.yml, so no version update PRs are generated; it is only recommended to enable Dependabot alerts while keeping security updates off. The licensing of third-party assets such as the demo site and screenshots must be verified separately; the code itself is under the MIT license.
Next.jsViteStarter
Is it right for your project?
Use Cases
- A monorepo starting point for AI coding agents with clear package boundaries and repository constraints
- Multi-package frontend projects that need unified lint, type checking, formatting, and dependency checks
- Teams that want to control the pace of dependency introduction using a pnpm catalog and supply-chain protections
- A continuous integration configuration reference for enabling CodeQL and secret scanning in public repositories
Suitable For
- Developers organizing multi-package projects with pnpm and Turborepo
- Teams that need to provide stable repository structure constraints for AI agents
- Frontend engineering teams concerned with dependency supply chains and secret leak checks
Getting started & customization
Use these recorded setup notes alongside the repository instructions for your chosen version.
- 1
Requires Node.js 24.21.0 (see .nvmrc) and pnpm 12.6.0 (see packageManager in package.json)
- 2
After running pnpm install, use pnpm dev to start the playground at http://localhost:3000
- 3
After using the template, it is recommended to rename the @repo/* scope and update the name and description in package.json
- 4
CodeQL requires GitHub Code Security for private repositories; if default setup is already enabled, it must be disabled first, otherwise workflow uploads will be rejected
- 5
secrets:scan requires gitleaks v8.19+ in PATH or a running Docker daemon
License & source material
Usage conditions & limitations
Free to use · keep license noticeThis entry covers the free version under the MIT license in a public repository; the free scope is the code of this version and does not mean that external services or third-party assets are free.
Must comply with when using
- You are allowed to use, modify, commercially use, and distribute the code of this version for free.
- When distributing copies or substantial portions of the code, retain the original author's copyright notice and the full MIT license notice.
- The code is provided as is; warranties and limitations of liability are governed by the original license and applicable law.
Additional costs & items to verify
- Demo images, fonts, icons, and other third-party assets must be checked against their respective licenses and cannot be judged solely by the code's MIT license.
- External services such as domains, hosting, databases, payments, or AI may incur separate charges.
- CodeQL code scanning is free only for public repositories; private repositories require GitHub Code Security (which may be a paid feature).
- If default setup is enabled under Settings → Code security, it must be disabled first, otherwise GitHub will reject workflow uploads.
- The secrets:scan command depends on gitleaks v8.19+ in PATH or a running Docker daemon.
- It is recommended to enable Dependabot alerts but keep Dependabot security updates off to avoid automatic PRs.
View Original Text Basis
Permission is hereby granted, free of charge
Original License Text
CodeQL (the `codeql` CI job) is free on public repos; private repos need GitHub Code Security.
Original README
If "default setup" is enabled under Settings → Code security, turn it off — GitHub rejects the workflow's uploads while it is on.
Original README
`secrets:scan` needs either `gitleaks` v8.19+ on PATH or a running Docker daemon.
Original README
https://github.com/valuecodes/agentic-monorepo-starter/blob/main/LICENSEhttps://github.com/valuecodes/agentic-monorepo-starter/blob/main/README.mdUnder Settings → Code security, turn on **Dependabot alerts** and leave **Dependabot security updates** off
Original README
Compiled by DeepSeek based on repository license and README ·2026-10-09. Results only cover the materials read; dependencies, images, fonts, and subsequent term changes are subject to their respective original texts.
Project checks & description sources
Template Information
- Source platforms
- GitHub
- Documentation and maintenance reference score
- More documented · 85 / 100
- Technologies
- Next.js · Vite · React
- Website type
- Starter
How this score is calculated
Our heuristic uses license records (up to 30), a demo link (12), a preview (10), stars (15), recorded maintenance (15), description completeness (8), feature records (5) and classification data (5). It is not a code, security or performance test, or a Google score. A link does not establish tested functionality.
What to verify for this project
- Repository update recorded
- 2026-10-09
- Screenshot last checked
- 2026-10-09
A demo link is listed. Check it with your own content and viewport sizes; its presence does not confirm that forms, authentication or payments work.
The catalog identifies Next.js as the primary stack. Check the actual dependency manifest and lockfile for versions and hosting requirements. These notes use recorded metadata, not a code audit or a deployment test.
Use a selection guide →How this description was prepared
AI-assisted description based on catalog records and repository material. Repository authors are not automatically the reviewers of this description.
Review declaration: [email protected] · 2026-10-09
Inspect the recorded source material
SHA-256: 1f8925f93346f75534fee871f8f5a6cf501cb5bd5dfa843128d204ec0b8a3ef0
2026-10-09T08:26:16.410Z
Source file / repository# Agentic Monorepo Starter A Turborepo template for agentic development: strict repo guardrails, consistent tooling, and clear package boundaries — so agents move fast without turning the codebase into spaghetti. ## What's inside - Vite playground in `apps/playground` (Vite 8, React 19, Tailwind CSS 4) - Shared tooling: oxlint, Knip, Prettier, TypeScript 7, Turbo - `@repo/logger` — structured JSON logging for Cloud Run / Cloud Logging - pnpm catalog for versions, with supply-chain guards: a 14-day release-age wait, a trust-downgrade check, and no git/tarball subdependencies - Claude Code settings in `.claude/` ```text apps/playground Vite 8 + React 19 sandbox packages/logger pino logger, Cloud Logging shaped JSON tooling/prettier shared Prettier config tooling/typescript shared tsconfig presets (base, node, react) tooling/github composite action: pnpm + Node + install; secrets-scan script .oxlintrc.json single root lint config for the whole repo ``` ## Getting started Requires Node.js 24.21.0 (`.nvmrc`) and pnpm 12.6.0 (`packageManager` in `package.json`). ```bash pnpm install pnpm dev # playground at http://localhost:3000 ``` ## Commands ```bash pnpm lint # type-aware linting, whole repo in one oxlint process pnpm knip # unused files, exports and dependencies pnpm typecheck # TypeScript 7 (tsc) across the repo pnpm test # test suite pnpm build # production builds pnpm format # Prettier write pnpm format:check # Prettier check (CI gate) pnpm secrets:scan # gitleaks secret scan over git history ``` oxlint prints nothing when there are no findings, so silent output means clean. CI runs typecheck, lint, knip, format-check, test, build and a gitleaks secret scan on push to `main` and on PRs, plus CodeQL code scanning. `secrets:scan` needs either `gitleaks` v8.19+ on PATH or a running Docker daemon. ## Use this template Use GitHub's **Use this template** button, then: - Optionally rename the `@repo/*` scope to your own (e.g. `@acme/*`) - Update `name` and `description` in `package.json` - Verify everything is green: `pnpm lint && pnpm knip && pnpm typecheck && pnpm test && pnpm build` - CodeQL (the `codeql` CI job) is free on public repos; private repos need GitHub Code Security. If "default setup" is enabled under Settings → Code security, turn it off — GitHub rejects the workflow's uploads while it is on. - Under Settings → Code security, turn on **Dependabot alerts** and leave **Dependabot security updates** off: you get notified about vulnerable dependencies without automatic PRs. There is deliberately no `.github/dependabot.yml`, so no version-update PRs either.
Explore similar templates
Compare previews and descriptions within the same stack and category.

Next.js SaaS Starter
The official Next.js SaaS starter template, integrating email/password authentication, Stripe Checkout subscriptions, a dashboard with user/team CRUD, basic Owner/Member RBAC, and activity logging.
Next.js · SaaS

Next.js Commerce
Vercel's officially maintained Next.js App Router ecommerce starter with deep Shopify integration, offering a complete product catalog, cart, and checkout flow. Core logic is modular for swapping backends, and community provider versions exist for BigCommerce, Medusa, and Saleor.
Next.js · E-commerce

Next-js-Boilerplate
A developer-first Next.js 16 starter with Tailwind CSS 4 and TypeScript, supporting both App Router and Page Router.
Next.js · Starter

tailwind-nextjs-starter-blog
A Next.js and Tailwind CSS blog starter template using Contentlayer for Markdown/MDX, with built-in SEO, code highlighting, and tags. It targets personal technical blogs and migration from Jekyll/Hugo to React, and supports one-click Vercel deployment.
Next.js · Blog

next-forge
next-forge is a Turborepo-based Next.js template maintained by Vercel, positioned as a starting point for SaaS products.
Next.js · Starter
SaaS-Boilerplate
SaaS-Boilerplate is an open-source SaaS starter template built with Next.js App Router, React 19, TypeScript, Tailwind CSS, and Shadcn UI.
Next.js · SaaS